Security Tools Generate Data · CyberHQ® Generates Answers
Cyber resilience
in the language of your business.
One command layer for cyber resilience and AI governance. CyberHQ® turns cyber risk, threat and compliance into financial and operational decisions. CyberHQ.ai shows how your people and agents use AI, and proves you have it under control.
Works with what you have. Designed to your environment.
Trusted By
THE QUESTIONS LEADERS ASK
From Cyber Resilience to AI, Answers You Can Defend
Existing tools leave the hardest questions unanswered. Select one to see what answers it.
- Cyber Resilience
- AI Governance
-
The board wants to know what a breach would cost and whether the business could keep running. A maturity score and a traffic light do not answer that.
- Informed Cyber GRC & Master Control Framework
- Threat modeling & simulation
- Executive reporting
-
Security budgets grow every year, but few teams can say what last year's spend bought in reduced financial exposure.
- Cyber Risk Quantification (CRQ Module)
- Strategy & Business Case Module
- Executive reporting
-
Compliance frameworks are annual and backward-looking. Passing an audit does not mean being protected against today's attacks.
- Threat modeling & simulation
- Cyber Risk Quantification (CRQ Module)
- Risk & issue management
-
Most security teams cannot see which AI tools are in use, what data is being sent, or whether a session is a person or an autonomous agent.
- Shadow AI discovery
- Actor classification: human or agent
- AI productivity analytics
-
CASB, DLP, and secure web gateways were built for documents and email. They were not built to understand AI model context.
- DLP on AI prompts & pastes
- Behavioral anomaly detection
- Exposure Chains (ALE)
-
GRC platforms attest to controls without live monitoring. Governance questions need to be answered with evidence, not assertions.
- AI framework evidence: ISO 42001, NIST AI RMF, EU AI Act, MITRE ATLAS
- AI-agent governance
- AI Security Score
- Informed Cyber GRC & Master Control Framework
- Threat modeling & simulation
- Cyber Risk Quantification (CRQ Module)
- Strategy & Business Case Module
- Risk & issue management
- Executive reporting
- Shadow AI discovery
- Actor classification: human or agent
- AI productivity analytics
- DLP on AI prompts & pastes
- Behavioral anomaly detection
- Exposure Chains (ALE)
- AI framework evidence: ISO 42001, NIST AI RMF, EU AI Act, MITRE ATLAS
- AI-agent governance
- AI Security Score
The board wants to know what a breach would cost and whether the business could keep running. A maturity score and a traffic light do not answer that.
Security budgets grow every year, but few teams can say what last year's spend bought in reduced financial exposure.
Explore CyberHQ® →Compliance frameworks are annual and backward-looking. Passing an audit does not mean being protected against today's attacks.
Explore CyberHQ® →Most security teams cannot see which AI tools are in use, what data is being sent, or whether a session is a person or an autonomous agent.
Explore CyberHQ.ai →CASB, DLP, and secure web gateways were built for documents and email. They were not built to understand AI model context.
Explore CyberHQ.ai →GRC platforms attest to controls without live monitoring. Governance questions need to be answered with evidence, not assertions.
Explore CyberHQ.ai →The Cyber Resilience Command Layer Your Stack Has Been Missing
CyberHQ® sits above your existing security ecosystem and connects every tool and data source via API. AI-assisted analysis turns those fragmented outputs into one continuously updated intelligence layer, so lean teams can reach defensible answers faster. It does not replace your existing tools. It makes sense of them.
Executive Report
Evidence That Holds
Evidence That Holds
The same outputs from the same inputs, every time. Defensible to a board, a regulator, or an auditor, and continuously maintained.
Up to 75%
reduction in manual compliance effort
Minutes
to produce board-ready reports
100 +
integrations across IT, OT, IoT, and GRC tools
Unlimited
supported security and AI frameworks
From Discovery Through to Board-Ready Governance
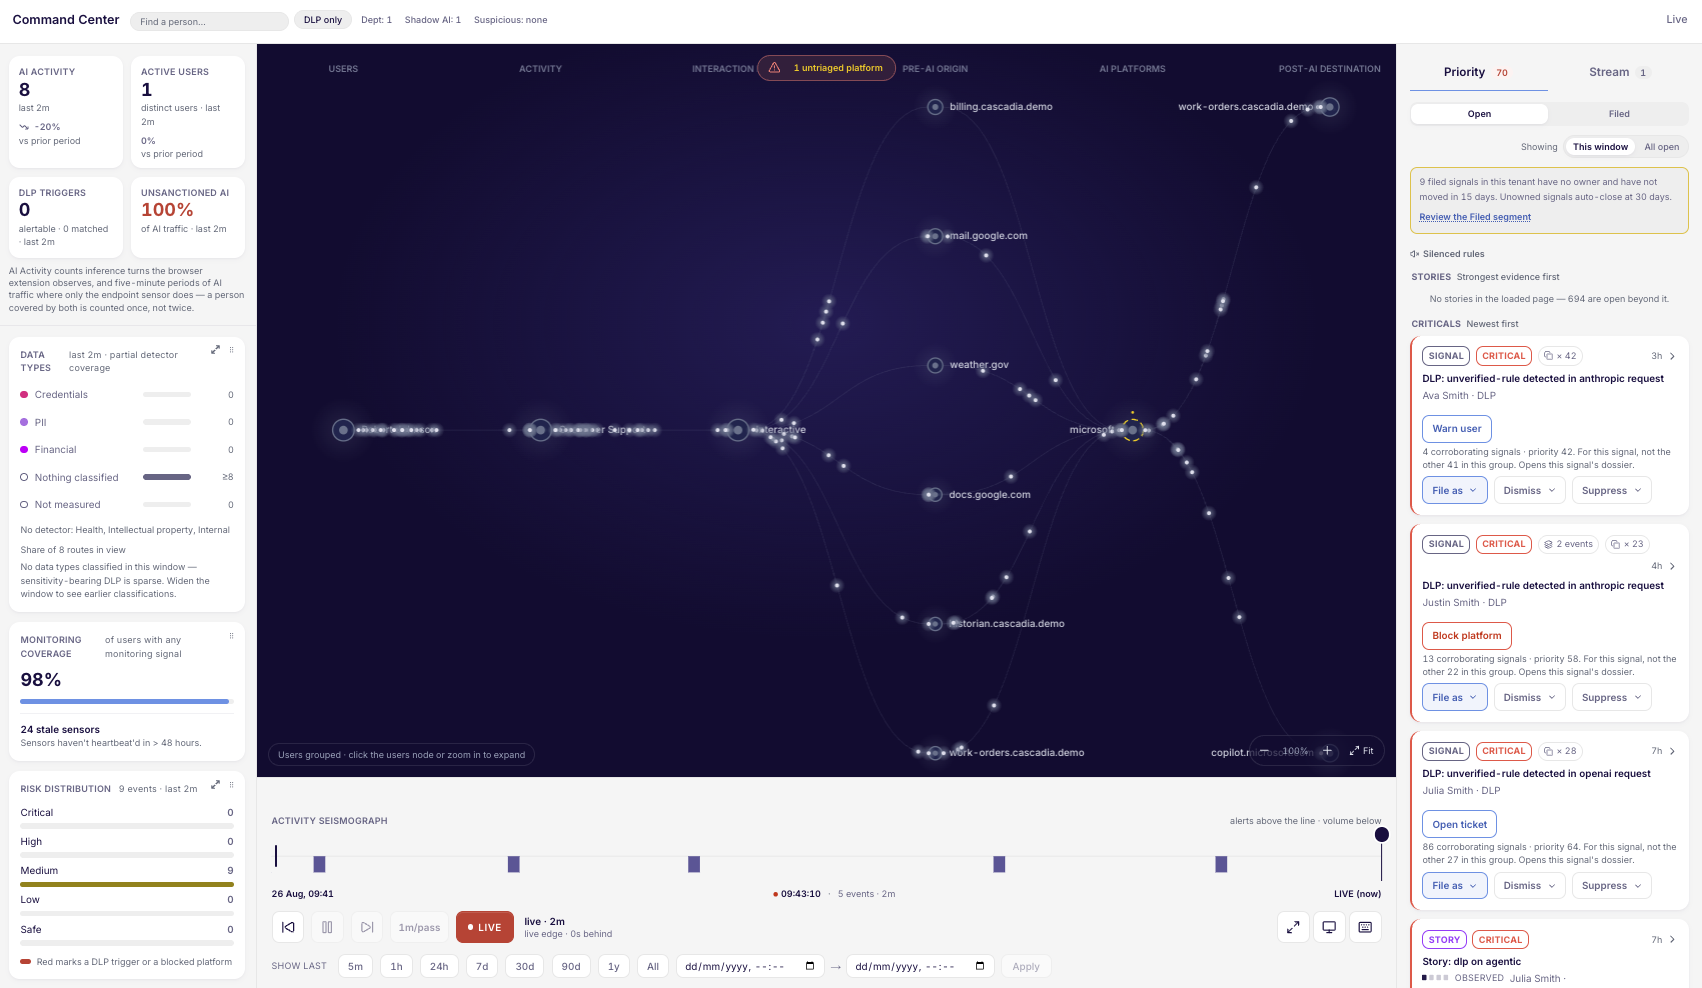
CASB, DLP, and secure web gateways were built for documents and email. CyberHQ.ai sits alongside them: live monitoring grounded in AI-specific context, feeding an attestation workflow with real evidence.
It does not replace your security stack. It adds the AI context it lacks.
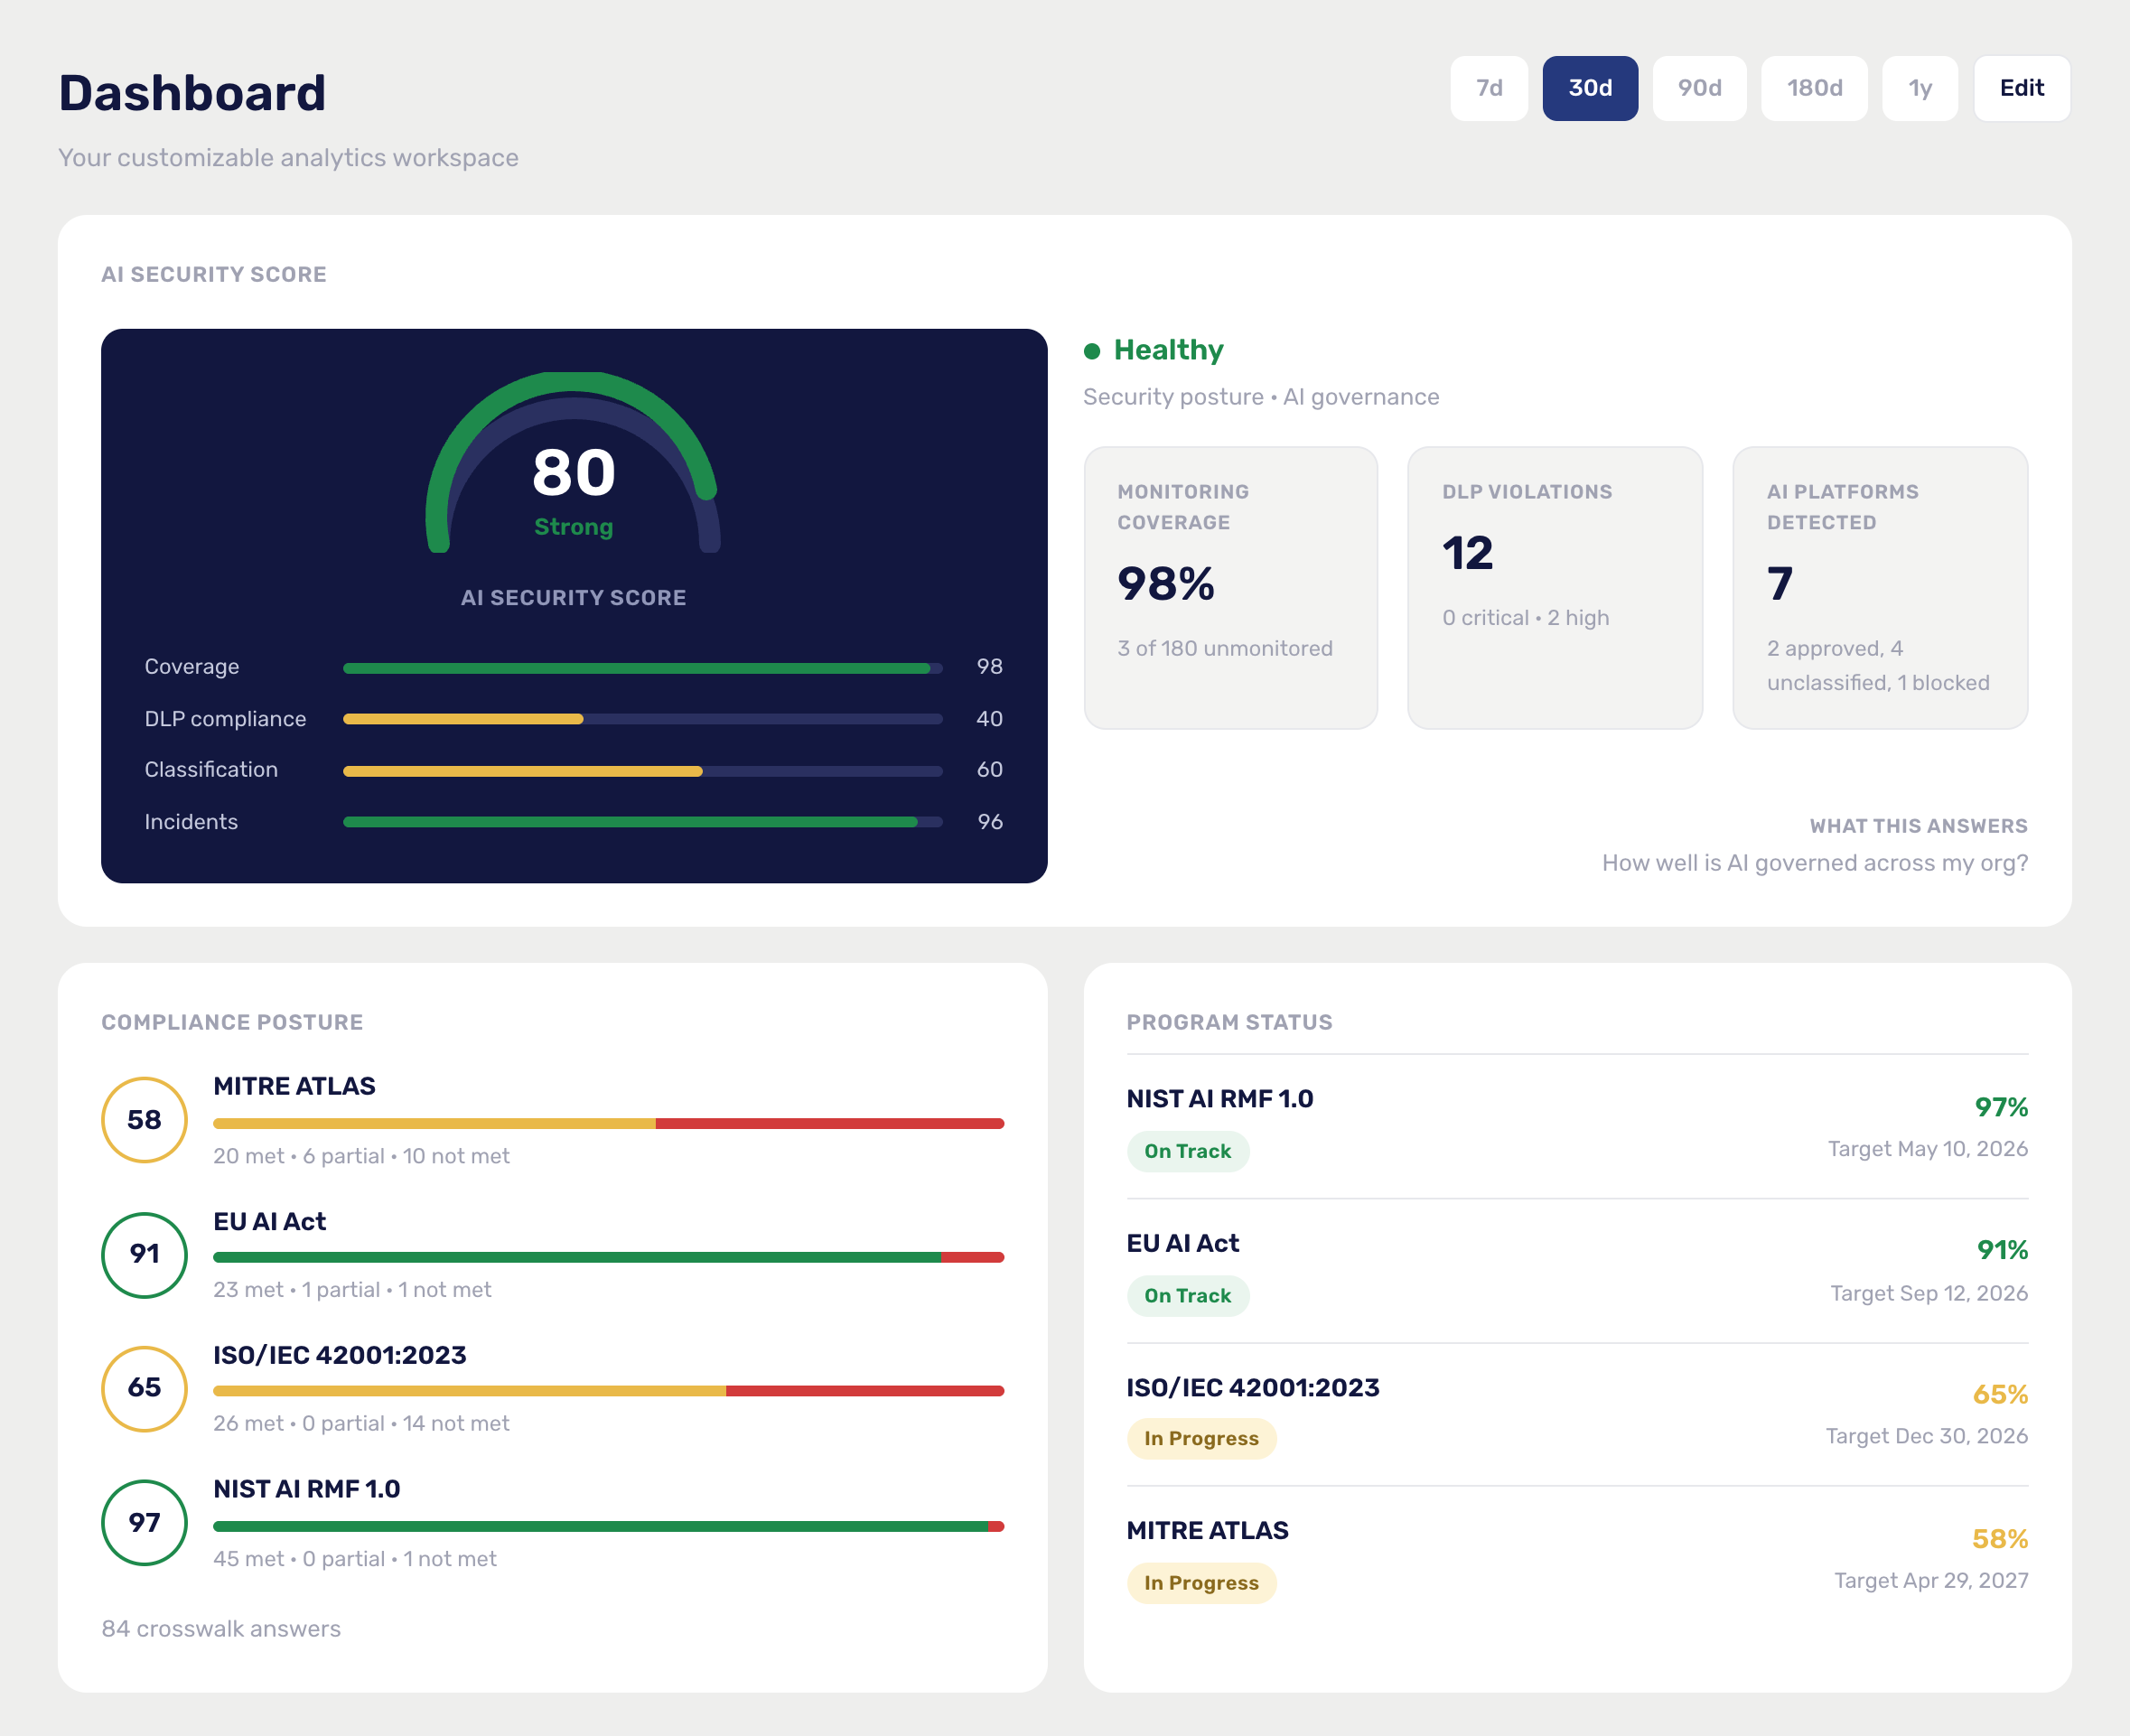
The AI security score stands at 35, down 45 points on 30 days ago. This is the band that warrants escalation.
< 30 mins
and a few clicks to deploy for control of your AI tools
24-48 hrs
typically to first meaningful DLP findings
Dynamic
detection and monitoring of known and unknown AI tools
Govern AI
ISO 42001, NIST AI RMF, EU AI Act and MITRE ATLAS
CYBERHQ®
Make Sense of Your Exisiting Security Tools
CyberHQ® is not a traditional security tool. It sits above your existing ecosystem — integrating with any system via API — to transform your fragmented data into a single, intelligence-driven decision layer.
It does not replace your tools. It makes sense of them.
CyberHQ® Connect
SIEM · EDR / XDR · Vuln Mgmt · Cloud Security · ITSM · Threat Intel · OT / ICS · GRC / Risk · IoT Security
Compliance → Defensible Resilience
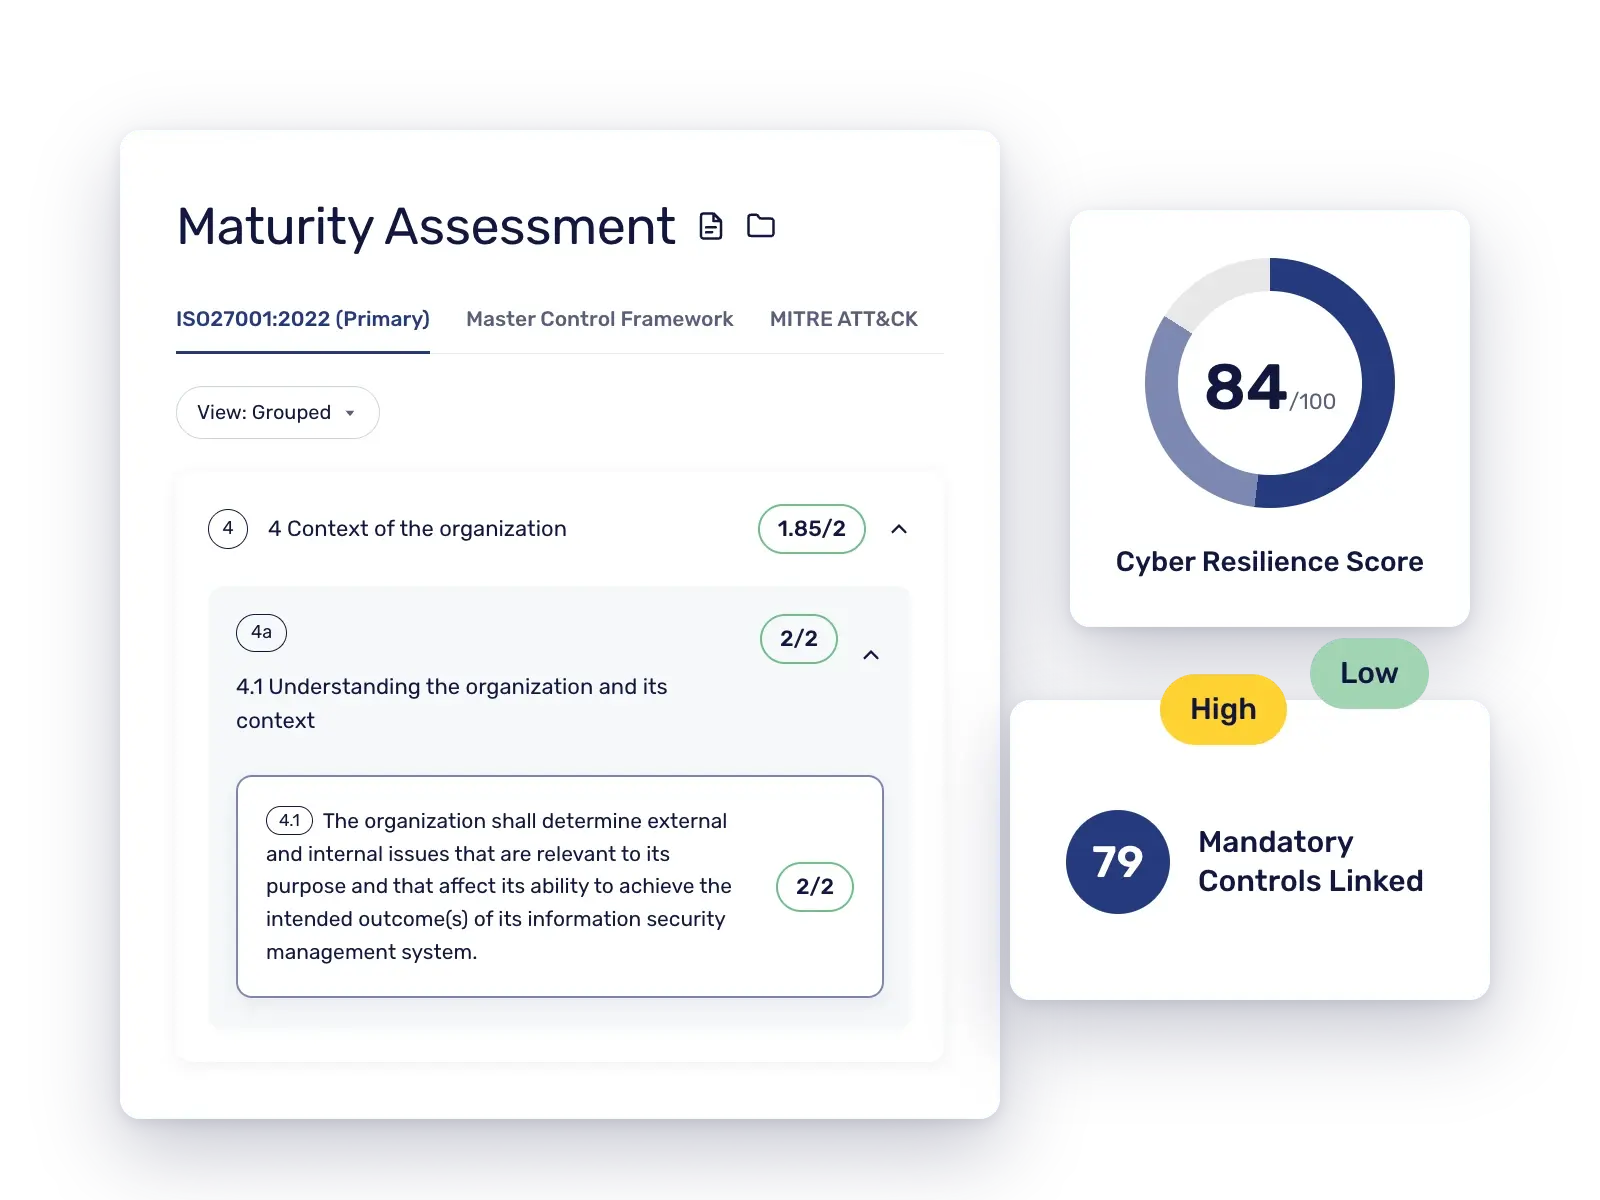
CyberHQ® reframes cybersecurity around service continuity and operational impact, moving it from a cost center to a strategic business function. Know, with evidence, how prepared your organization is and how quickly you can recover.
Compliance that reduces real-world risk
Know, with evidence, how prepared your organization is before an incident tests it
Move cybersecurity from a cost center to strategic business function
Technical Noise → Financial Clarity
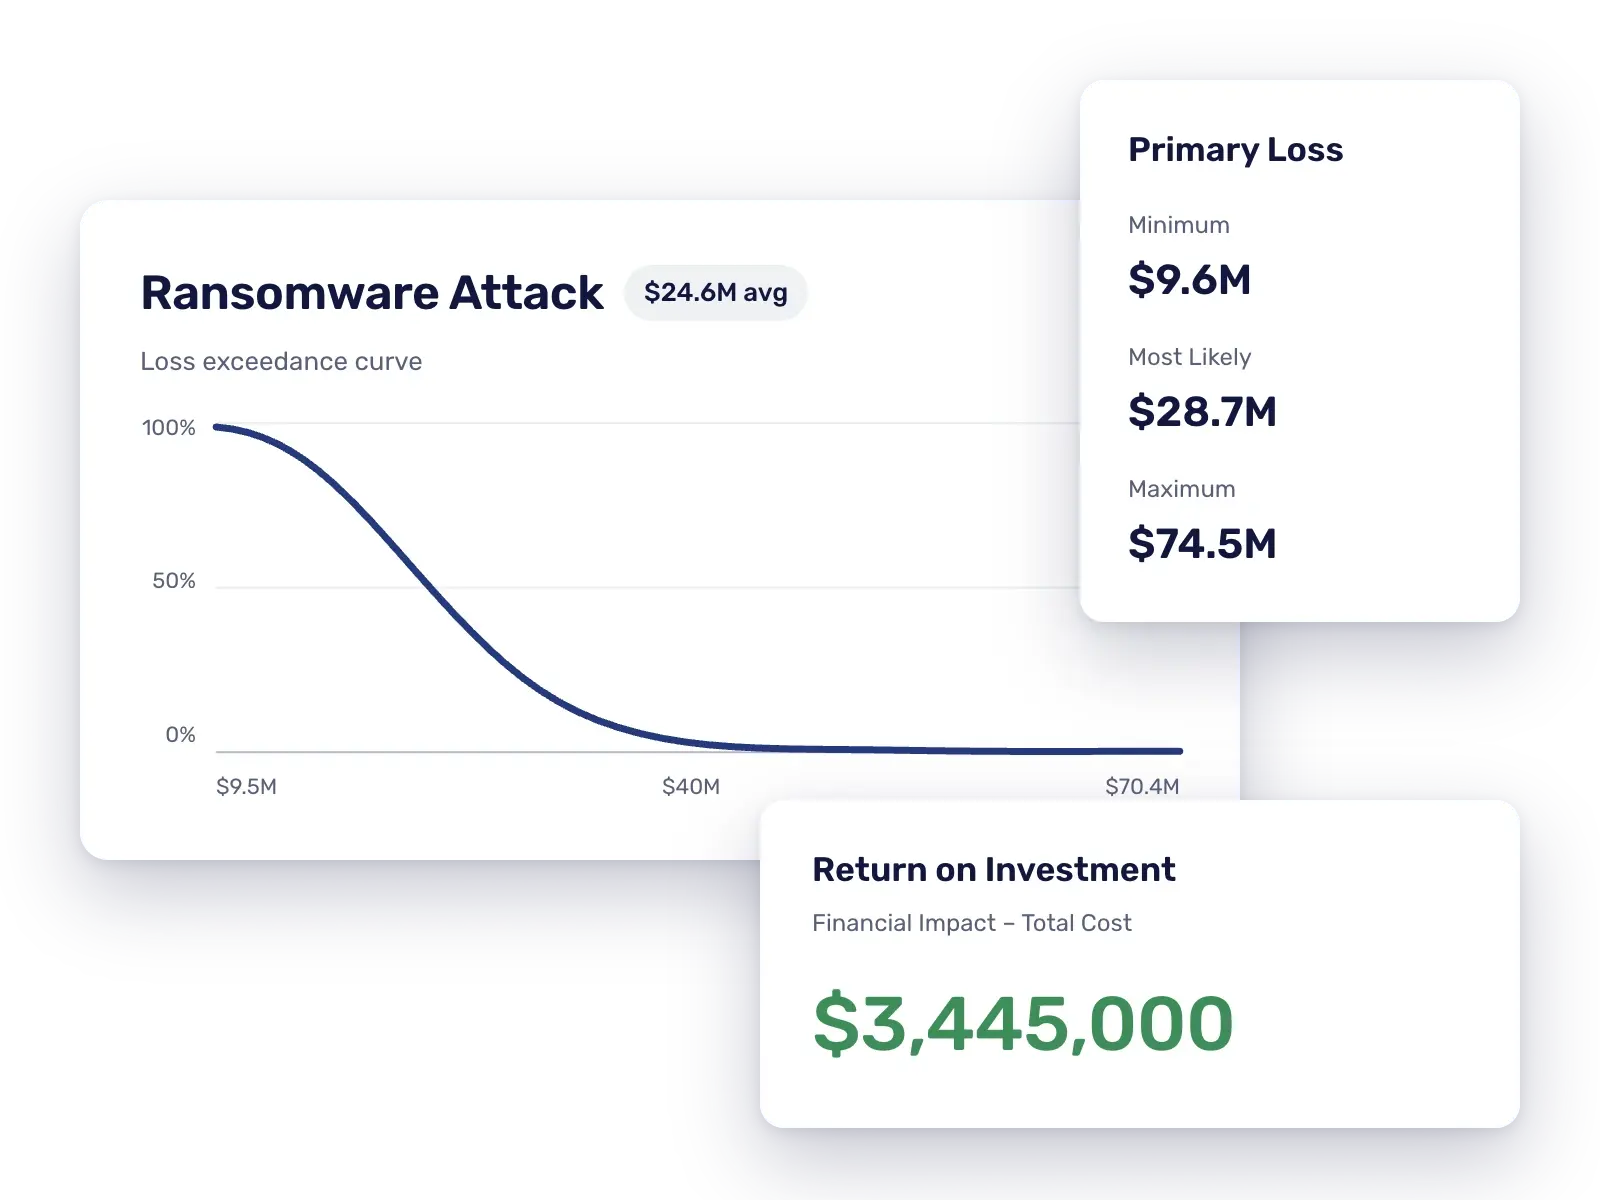
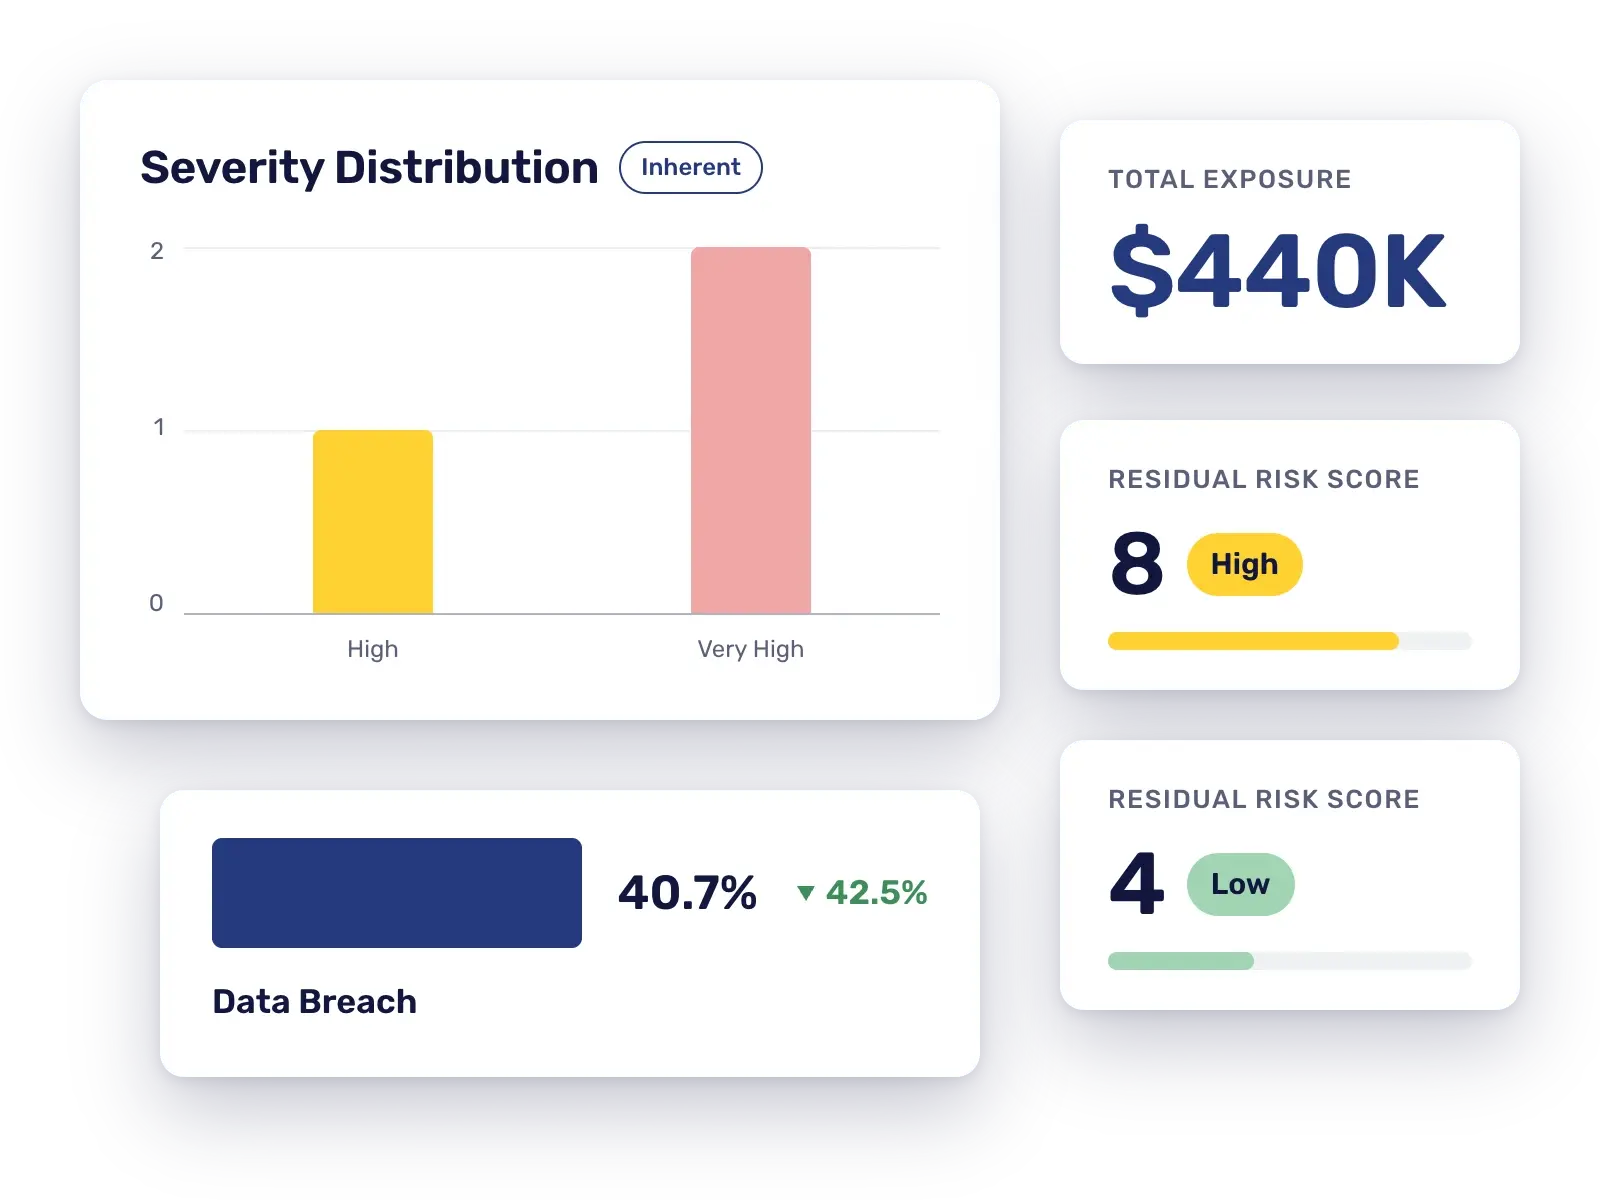
Alerts, vulnerabilities, and control scores become financial exposure, business risk, and investment decisions. CyberHQ® quantifies cyber risk in monetary terms so every conversation with the board is backed by data.
Cyber risk expressed in financial terms so your investment decisions are backed by data, not intuition
Every board conversation backed by quantified monetary exposure
Know which investments reduce the most risk per dollar
Siloed GRC → Operational Decision Engine
Traditional GRC is static, backward-looking, and disconnected. CyberHQ® is real-time, integrated, and decision-focused, connecting risk, threat, compliance, and business context into a unified command layer.
Compliance posture always current, not a last-quarter snapshot
Connect risk, threat, compliance, and business-context in one command layer
Board-ready reporting generated automatically
Protect Everything → Protect What Matters Most
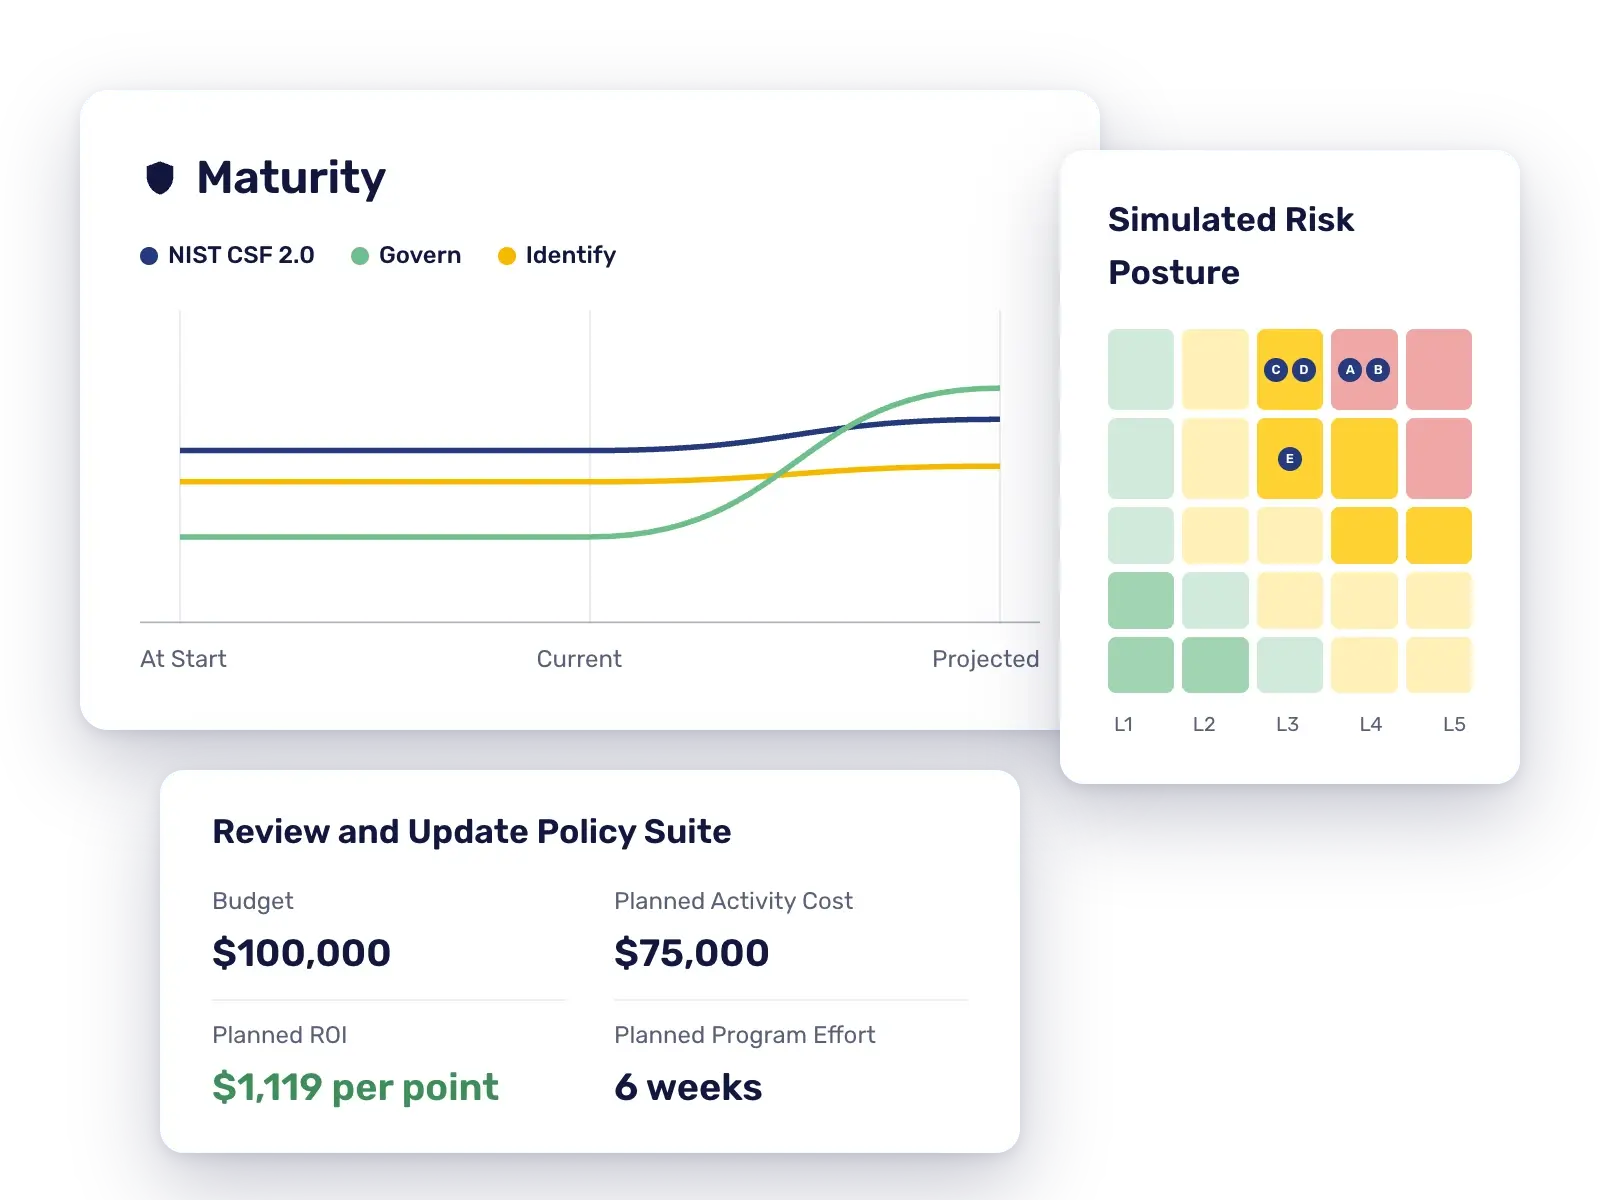
Not everything can be protected equally and not everything should be. CyberHQ® enables service-centric prioritization and risk-based investment allocation based on what actually matters to your business.
Actions ranked by business impact and financial exposure, not technical severity
Protect the services that drive continuity and revenue
Identify where spend overlaps or underprotects and reallocate with confidence
We Think We Have Control → Here Is the Proof
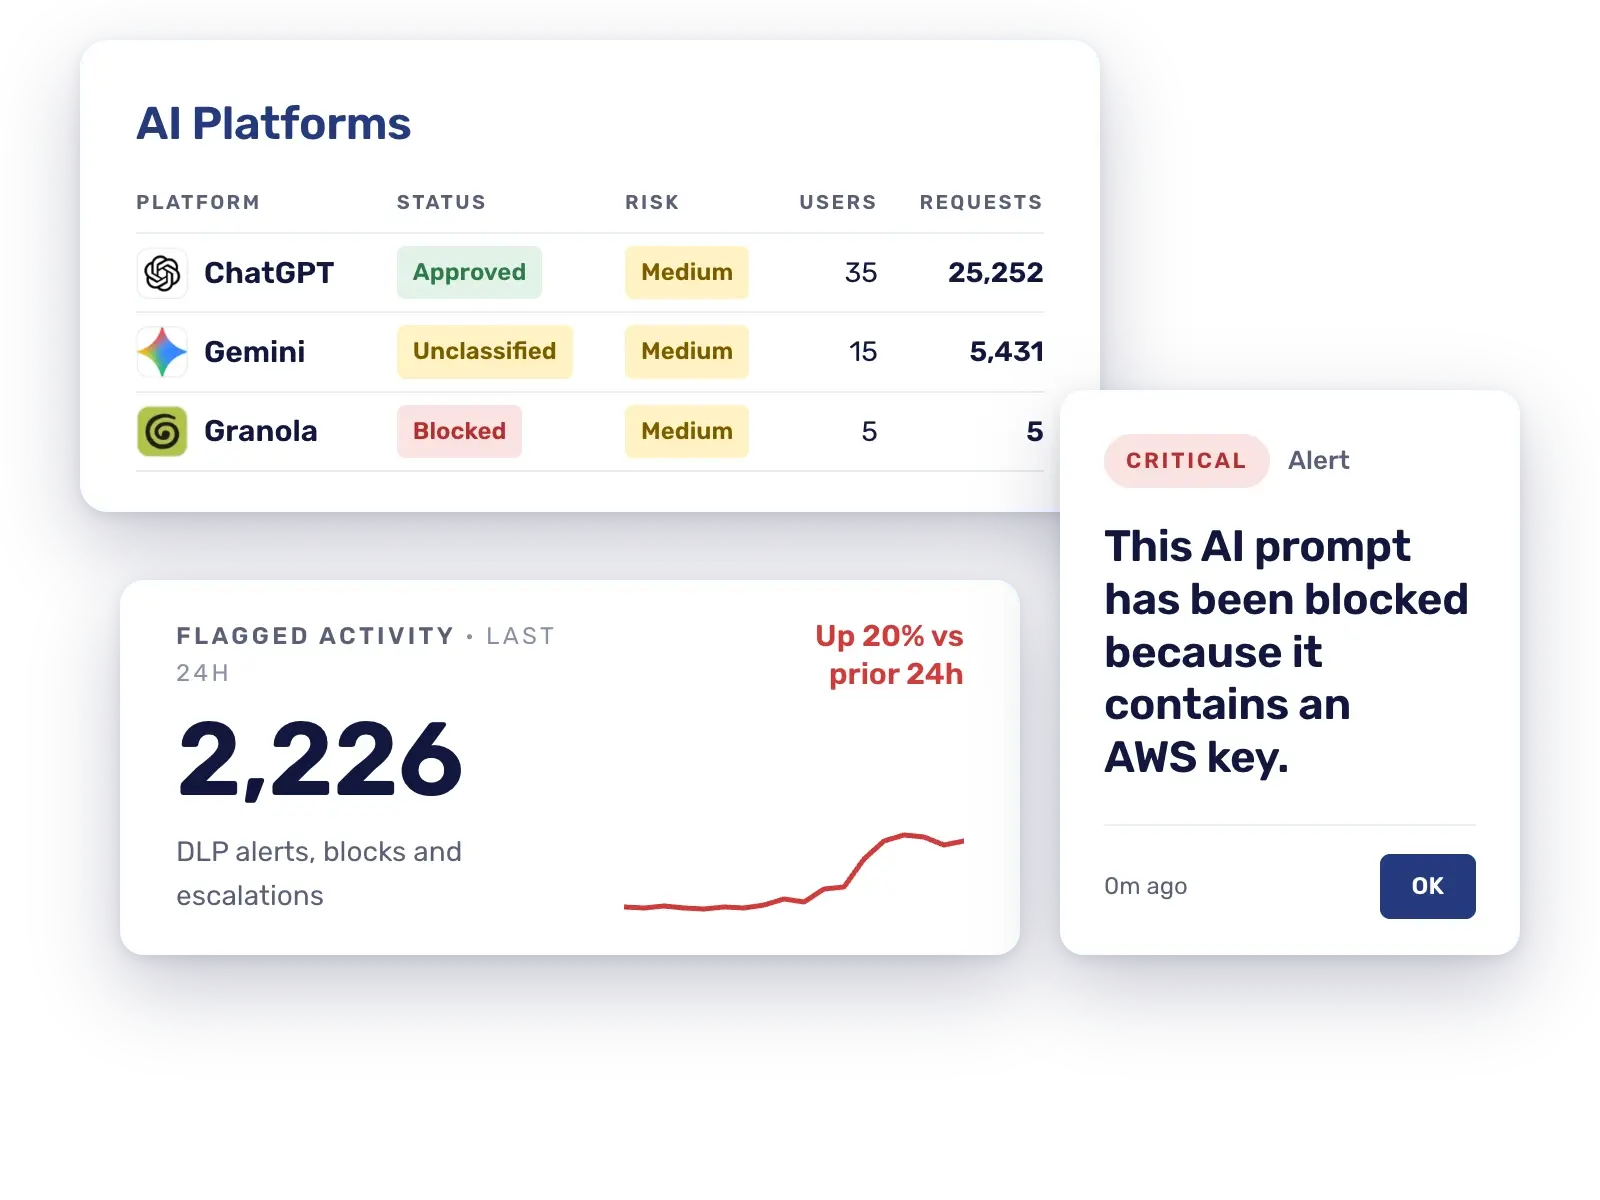
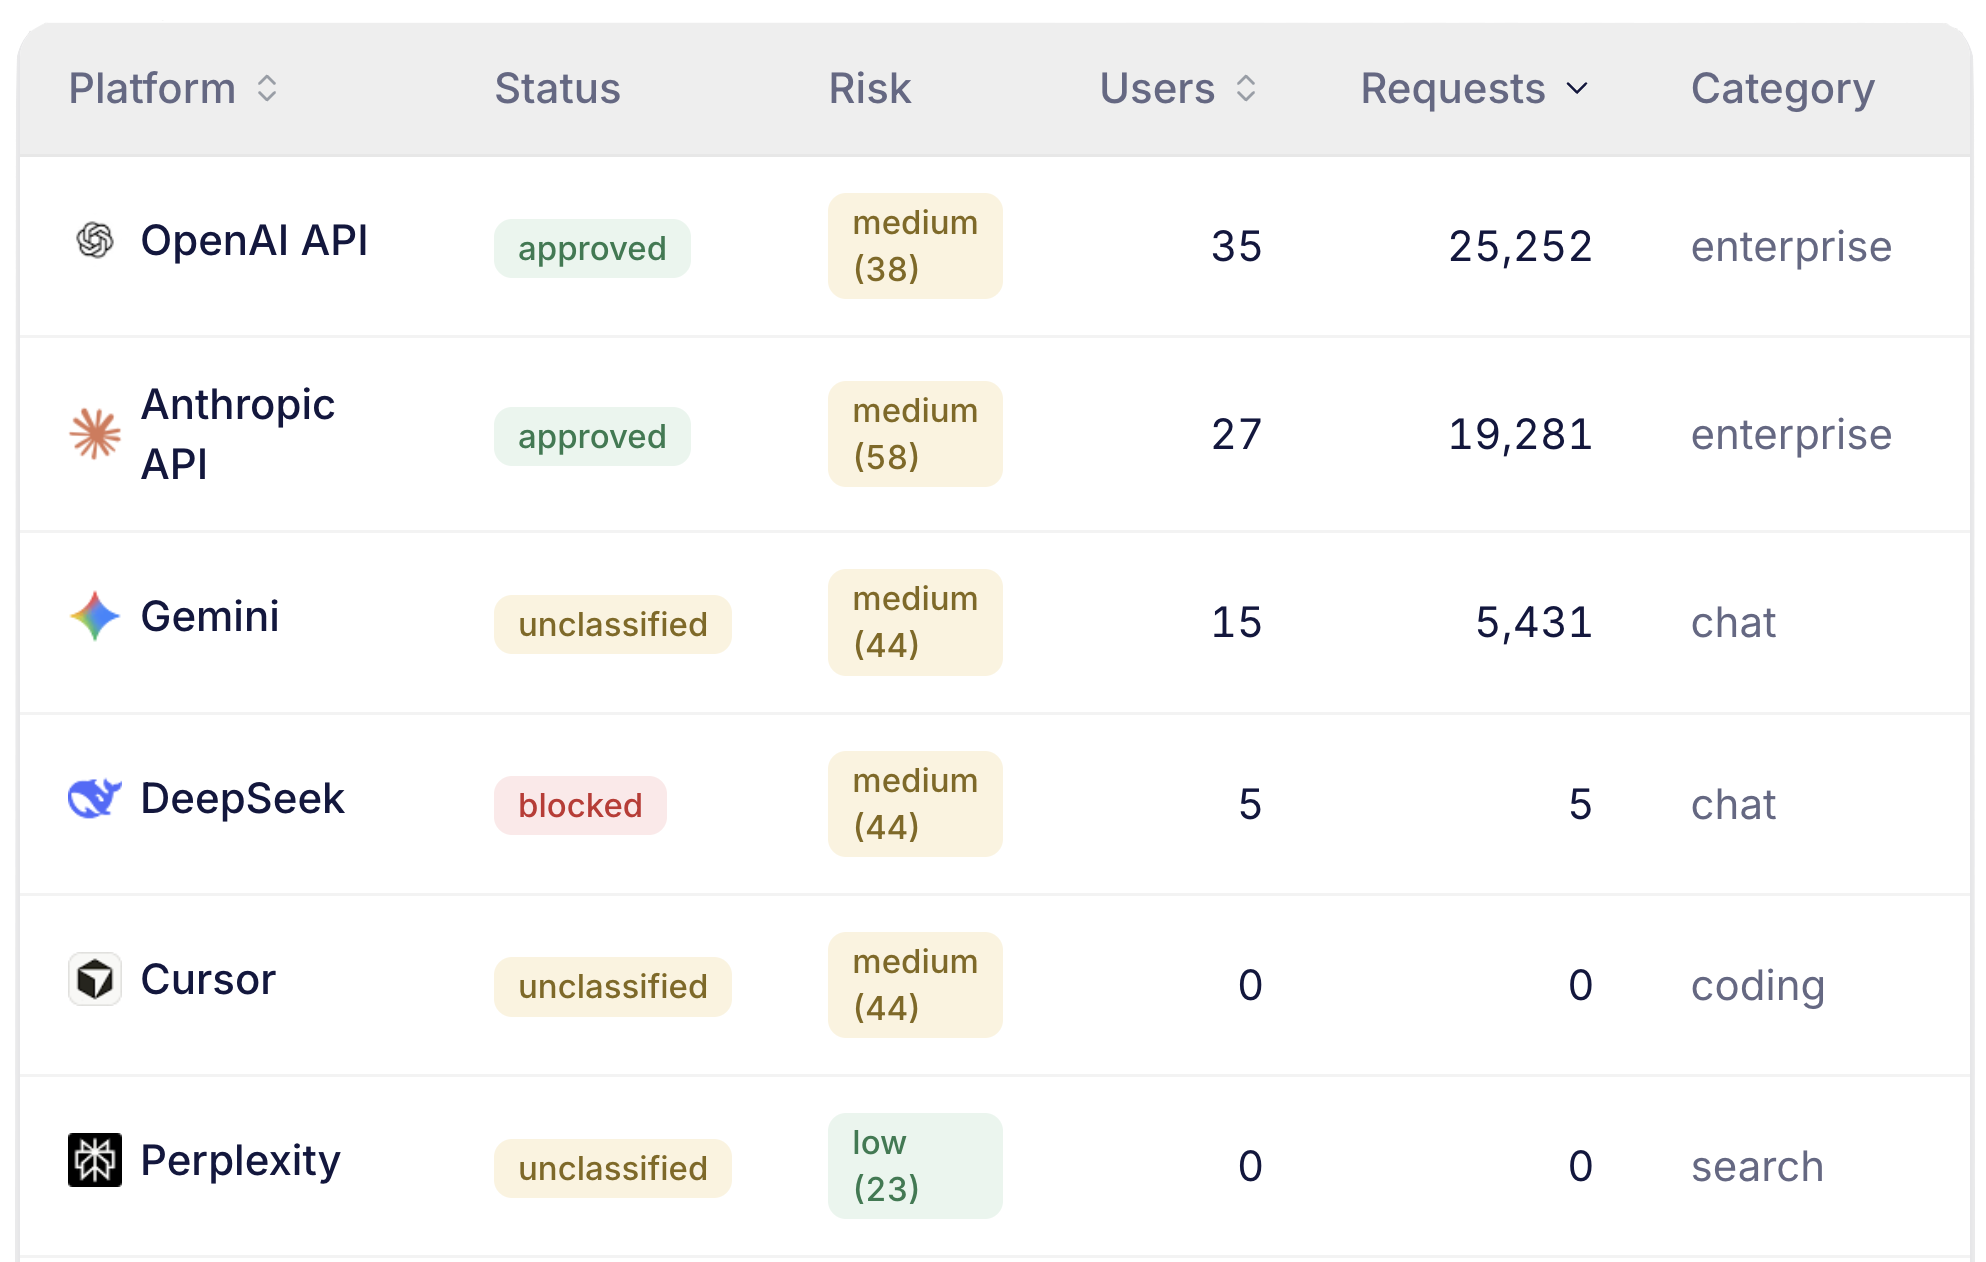
Finance, legal, HR, customer service, and operations are all using ChatGPT, Claude, Gemini, Microsoft Copilot, Cursor, and dozens more. Most security teams cannot see which tools are in use, what data is being sent, or whether a session is a person or an autonomous agent.
Reveal unapproved AI tools and which sessions are driven by a human or an autonomous agent
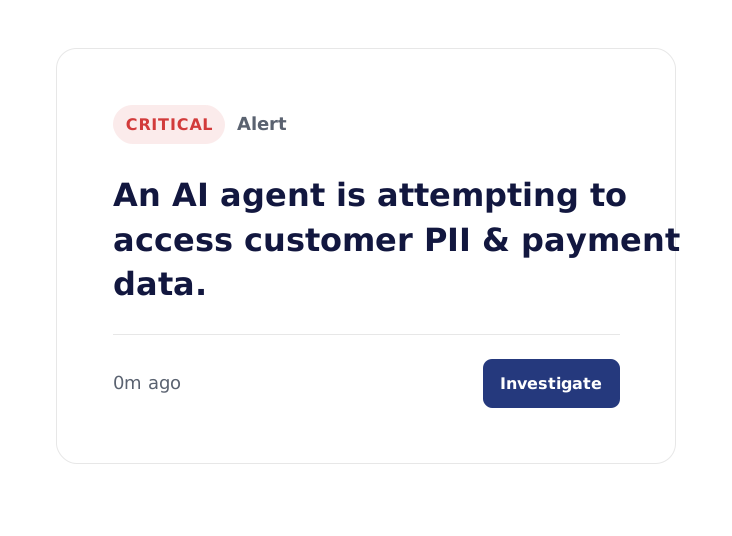
An alert fires when credentials or customer data are pasted into an AI too
Governance questions are answered with real evidence
How They Work Together
Two Streams of Evidence.
One Answer for the Board.
CyberHQ.ai captures what is happening with AI, live. CyberHQ® puts it in financial and operational context alongside every other cyber risk.
Start with either: CyberHQ.ai is licensed per user alongside any CyberHQ plan, and its REST API connects to CyberHQ® for full GRC.
CyberHQ.ai
What is happening with AI
Shadow AI, data sent, agents running, provider risk, and framework evidence, captured at the browser and endpoint.
CyberHQ®
What it means for the business
Quantified exposure, critical services, investment decisions, and board reporting, across IT, OT, IoT, third parties, and AI.
What Our Customers Say
“By utilizing CyberHQ® as a command layer, we can help leaders move away from tactical noise and toward a clear, financial understanding of their cyber posture.”
James Pearce
Vice President, Global Consulting & Implementation, NCC Group
“It’s the engine room for my team to be able to understand all the various moving parts when it comes to security”
Dr Kevin Tham
Chief Information Security Officer, RDC.AI
"CyberHQ® puts everything in one place, our maturity, risks, issues, and improvement programs and makes it easy to show exactly how our initiatives reduce risk and improve posture"
Andrew Bullen
Manager of Cyber Security, St John WA
“Every day I can log in and see where my team and I need to focus our efforts. It provides us with better reporting capabilities on risks and improvement opportunities that I can easily share with business executives."
CPA Australia
Frequently Asked Questions
What is CyberHQ®?
CyberHQ® is Avertro's Cyber Resilience Command Platform. It sits above your existing cybersecurity stack, connects your tools via API, and transforms fragmented data into a unified intelligence layer. As a result, it enables you to quantify risk, prioritize investments, and govern cyber as a strategic business function.
Can CyberHQ® quantify cyber risk in financial terms?
Yes. CyberHQ®'s Cyber Risk Quantification (CRQ) capability translates cyber threats into monetary exposure using industry-standard loss models and your organization's specific business context.
What is CyberHQ.ai?
CyberHQ.ai is Avertro’s AI Security Command Platform. A Chrome and Edge browser extension and a native endpoint sensor give security teams a continuous, evidence-backed picture of how the organisation uses AI, from first shadow-AI discovery through cost governance, AI-agent oversight, and audit-ready compliance.
How long does implementation take?
CyberHQ® is designed for rapid, low-friction deployment. CyberHQ® Connect's pre-built API connectors enable real-time data ingestion without disrupting your existing tools or workflows.
CyberHQ.ai deploys in under 30 minutes, with no proxy at any tier, and typically delivers its first meaningful DLP findings within 24 to 48 hours.
Does CyberHQ® support my compliance frameworks?
CyberHQ® supports unlimited security and AI frameworks, plus custom variations, including NIST CSF, ISO 27001, SOC 2, Essential Eight (AU), DORA (EU), NIS2 (EU), and more. The Master Control Framework holds over 1,800 controls: assess a control once and it counts towards every framework you run.
How is CyberHQ® different from traditional GRC platforms?
Traditional GRC platforms are static, backward-looking, and focused on compliance tracking. CyberHQ® is real-time, integrated, and decision-focused, connecting risk, threat, compliance, and business context into a single command layer.
Do I need CyberHQ® to use CyberHQ.ai?
Do I need CyberHQ® to use CyberHQ.ai?
No. Each product can be used on its own. CyberHQ.ai is licensed per user alongside any CyberHQ plan, and the same API connects it to CyberHQ® for full GRC.
What environments does CyberHQ® support?
What environments does CyberHQ® support?
CyberHQ® provides unified cyber risk visibility across IT, OT (operational technology / ICS), and IoT environments.
CyberHQ® • CyberHQ.ai
See It Configured to Your Environment
Book a 30-minute interactive session to see how CyberHQ® and CyberHQ.ai integrate with your existing tools, frameworks and environment.
No Commitment Required.